本帖最后由 t0p丶邓 于 2017-12-15 09:45 编辑
首先说明下为什么写这么个脚本,这里引出个应该大部分人都知道了的sql注入绕过方法
一般的waf对GET,POST,上传表单的数据过滤都有不同的规则,因为考虑到文件内容的原因,部分waf对上传表单处的过滤没POST,GET请求那么严
但是很多网站的post数据是支持通过表单方式提交的,为了方便将POST的数据转成表单的样式提交于是写了这么小玩意
<html>
<body>
<meta http-equiv="Content-Type" content="text/html; charset=utf-8" />
<title>POST注入转表单提交数据小脚本</title>
<form action="sql.php" method="post"
enctype="multipart/form-data">
<label for="sql">Fuck:</label>
<input type="text" name="url"/>
</br>
<label for="parm">POST数据:</label>
<input type="text" name="parm"/>
</br>
<input type="submit" name="submit" value="千年杀" />
</form>
<?php
$id=@$_POST['url'];$parm=@$_POST['parm'];
$arr=explode("=",$parm);
$arr2=explode("&",$parm);
$num=count($arr2);
if($num>1){
$arr01=explode("=",$arr2[0]);
for($number=0;$number<$num;$number++){
$n[$number]=explode("=",$arr2[$number]);
}
}
?>
<form action=<?php echo $id;?> method="post"
enctype="multipart/form-data">
<input type="text" name=<?php echo $arr[0];?> value=<?php echo $arr[1];?> /></br>
<label for="parm">单参数请点击:</label>
<input type="submit" name="submit" value="submit" />
</form>
</br></br>
<form action=<?php echo $id;?> method="post"
enctype="multipart/form-data">
<input type="text" name=<?php echo @$n[0][0];?> value=<?php echo @$n[0][1];?> /></br>
<input type="text" name=<?php echo @$n[1][0];?> value=<?php echo @$n[1][1];?> /></br>
<input type="text" name=<?php echo @$n[2][0];?> value=<?php echo @$n[2][1];?> /></br>
<input type="text" name=<?php echo @$n[3][0];?> value=<?php echo @$n[3][1];?> /></br>
<input type="text" name=<?php echo @$n[4][0];?> value=<?php echo @$n[4][1];?> /></br>
<input type="text" name=<?php echo @$n[5][0];?> value=<?php echo @$n[5][1];?> /></br>
<input type="text" name=<?php echo @$n[6][0];?> value=<?php echo @$n[6][1];?> /></br>
<input type="text" name=<?php echo @$n[7][0];?> value=<?php echo @$n[7][1];?> /></br>
<input type="text" name=<?php echo @$n[8][0];?> value=<?php echo @$n[8][1];?> /></br>
<input type="text" name=<?php echo @$n[9][0];?> value=<?php echo @$n[9][1];?> /></br>
<label for="parm">多参数请点击:</label>
<input type="submit" name="submit" value="submit" />
</br>
</form>
</body>
</html>
 sql.php
(2.04 KB, 下载次数: 1402)
php只看了点视频还没看完==不会什么高端写法,自己将就着用下
下面贴下测试效果图
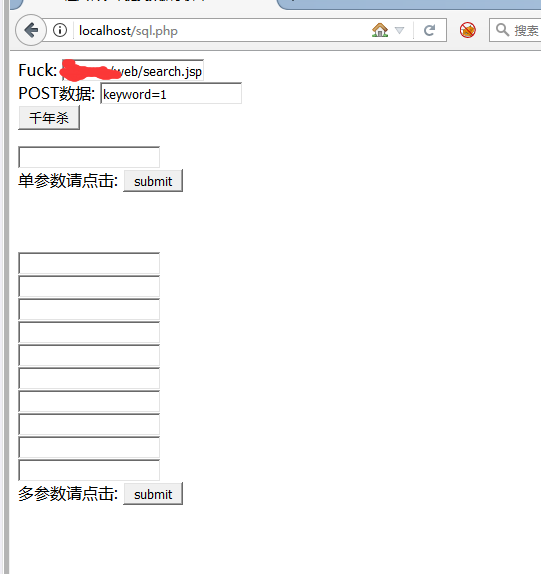
URL与POST数据分开提交,点击“千年杀”自动对参数个数进行检测并处理,单个参数点击下面那个提交,多参数点击最下面那个,只写了10个,更多参数可以自己添加
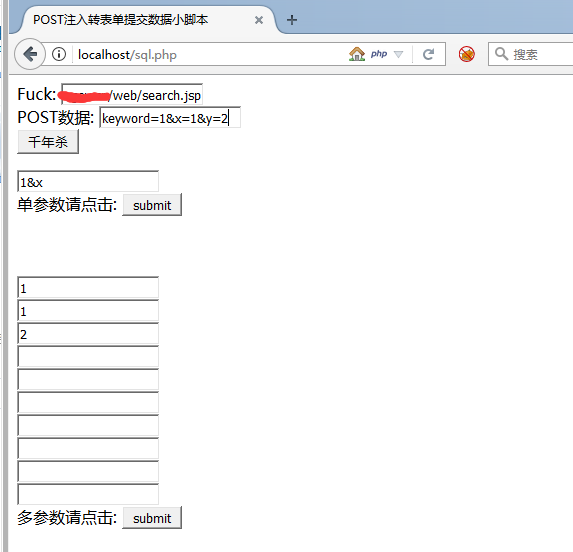
这是提交后burp抓包结果
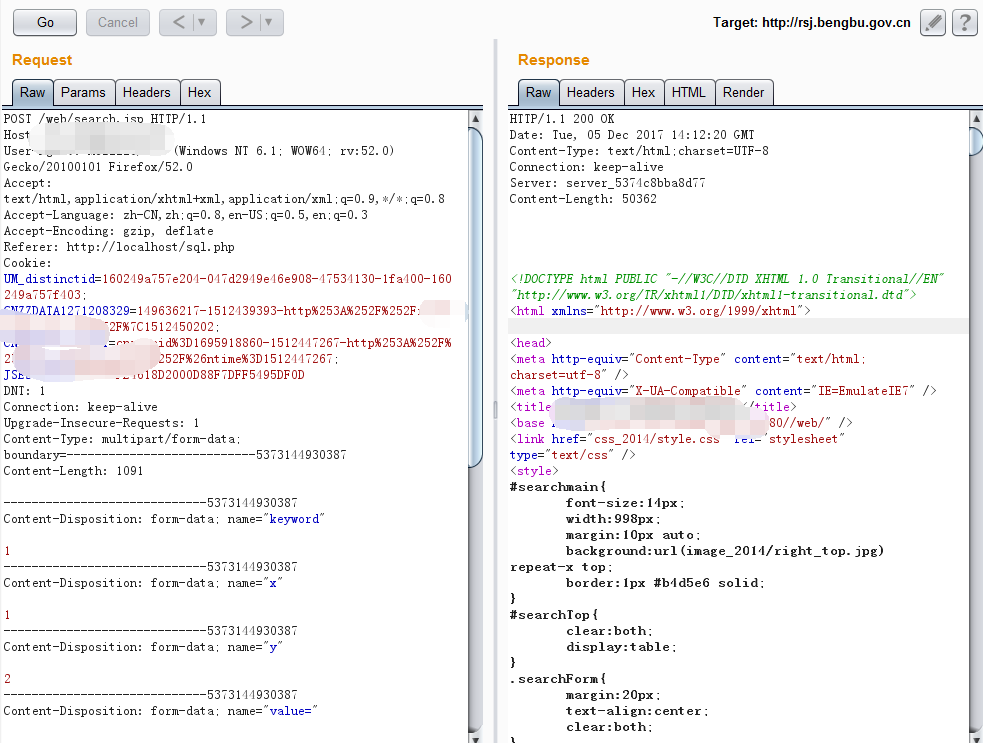
与正常POST提交对比一下
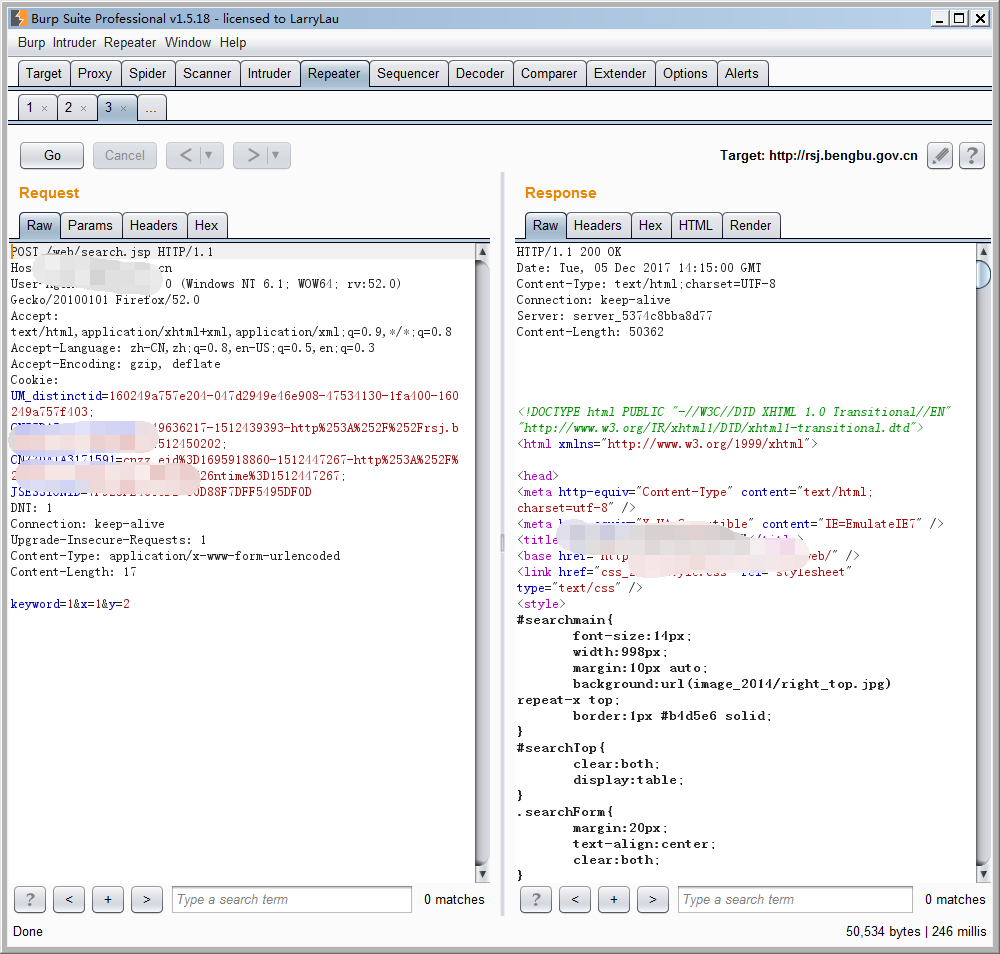
看起来没有任何差距,但是其实说不定已经绕过很多waf的限制了
这时候再配合一下以前不能绕过的payload尝试提交一下说不定就将军了呢==
至于payload什么的就不多发了,有兴趣的可以去土司看一下我写的几篇关于waf绕过的文章 土司id 11521 t0p丶邓
|
